
Deployment stalls for more reasons than model selection
Drafting proposals, searching internal policies, summarising contracts — there are countless situations where employees want to use generative AI. Yet simply providing a convenient service is not enough to make it stick. Every time someone wonders "Can I type the client's name here?" or "Is this document confidential?", work stops.
On the other hand, an outright ban leaves employees without the support they need and may push usage toward personal accounts the company cannot monitor. When planning a deployment, structuring clear rules and routing — not just selecting a capable model — is equally important.
This series explains "Hybrid Private AI" — combining cloud AI with an enterprise-managed AI platform — from concept through operations. Configurations using IMMERSIA are included as examples. Placing a specific device does not automatically deliver every capability described here.
Cloud and on-premises each have their role
Cloud AI means using AI delivered as an external service. On-premises means running systems in an environment you manage — your own facility. Required infrastructure, usage terms, and operational burden differ by model and use case.
Cloud AI is a candidate for organising publicly available information or processing data approved for external transmission. However, enterprise contracts and consumer services must not be treated as equivalent. Verify data retention, use for training, processing region, deletion, and administrative features for each service and contract.
On-premises AI is a candidate for information that must not leave the organisation, or for processing that requires tight integration with internal systems. In return, you must design who handles updates, monitoring, backups, and vulnerability response. "Cloud is risky, on-premises is safe" is an oversimplification that misses real risks.
Same interface, routing determined by information type
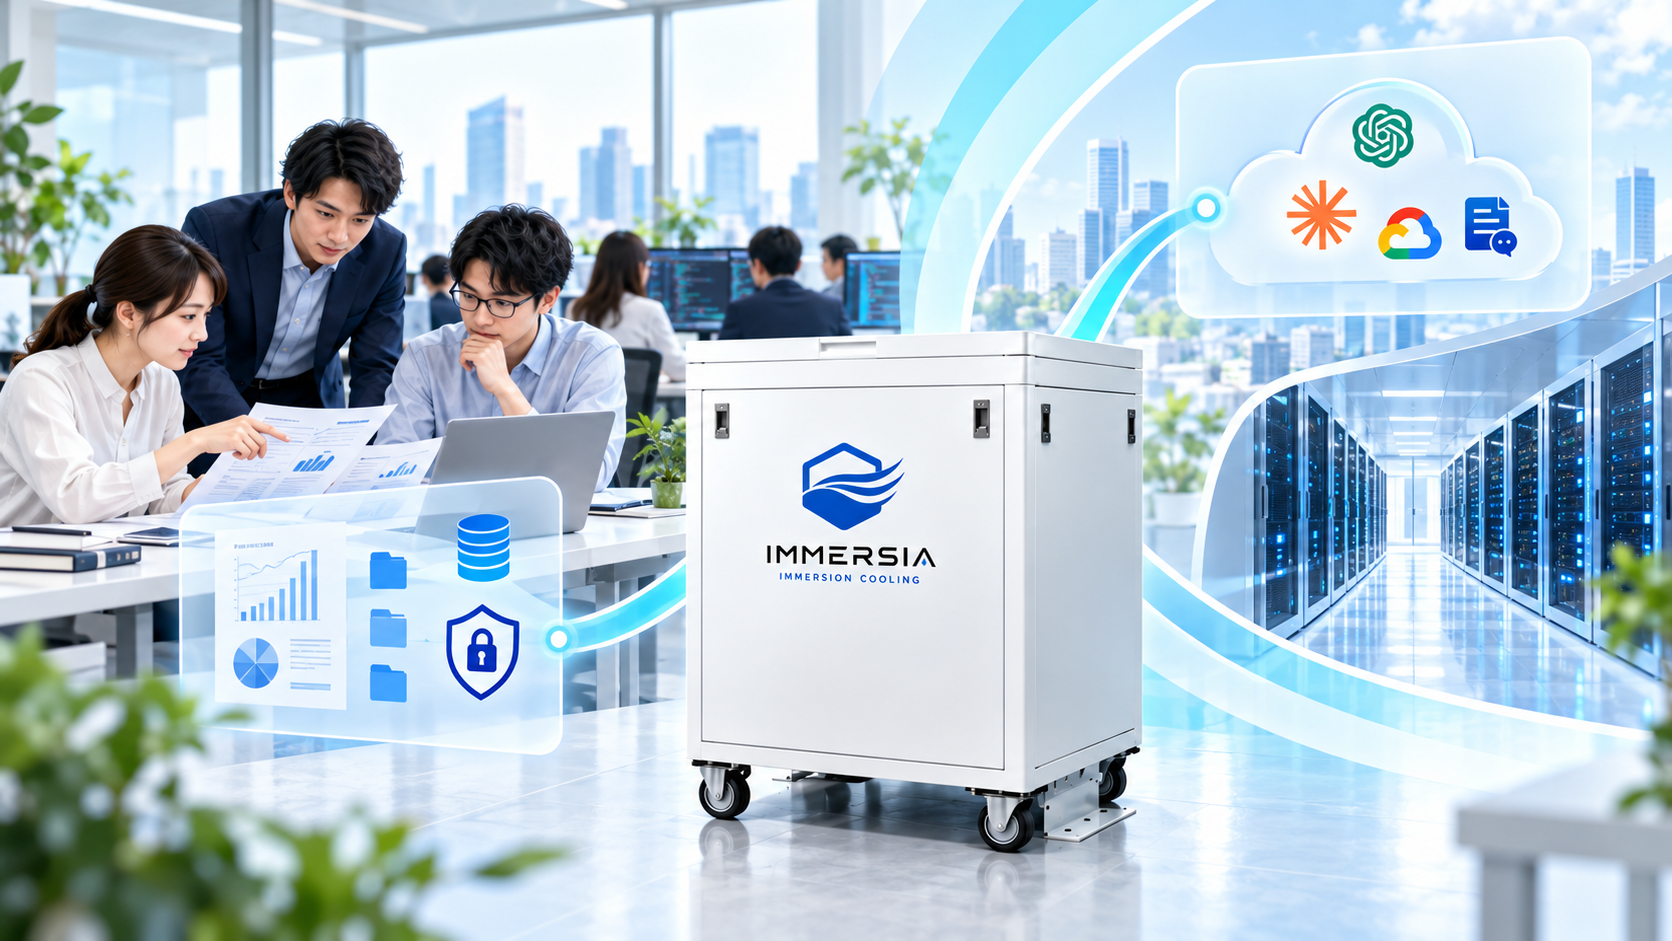
The goal of a hybrid configuration is for employees to use a single entry point while the system routes requests according to company policy. A request to tidy up published product information and a request to draft a proposal containing unpublished pricing require different permitted destinations.
In the example configuration, a unified AI workspace sits in front of a layer that checks information classification and user permissions. Information approved for external transmission goes to an approved cloud connection; information handled internally goes to the on-premises AI. Content that cannot be classified is held pending review.
Critically, AI classification results alone must not be the sole decision factor. Document classification, user department, contractual constraints, and approved recipient lists are all combined. Even a "general question" must be reviewed as a whole if attached files or conversation history contain confidential information.
Cloud AI
Organising public information and processing approved data. Verify contract terms, processing region, and training use.
On-Premises AI
Information that must not leave the organisation and tight internal-system integration. Design update, monitoring, and vulnerability response.
Hybrid Configuration
Automatic routing from a single entry point. Combine multiple conditions — do not rely on AI classification alone.
Routing is determined automatically by information classification and user permissions.
Start by mapping information types to tasks
Rather than targeting the whole organisation from the start, choosing one specific task makes design easier. For a sales team: summarising public materials, referencing internal price lists, and drafting customer proposals are three separate tasks with different information handling.
Then confirm: who uses it, what is referenced, who receives the output, and what may be sent externally. Reading a document yourself and passing it to an external service are different decisions. "I can view it" does not mean "I can transmit it."
An easily overlooked point is where the output goes. Even a summary created entirely in-house reaches the outside if sent directly to a customer. Include output review and sharing methods in the workflow, not just input controls. Seeing the full path from information entry to post-use moves AI deployment from tool addition to operational design.
Immersion cooling is an infrastructure option for on-premises AI
Running AI on-premises requires confirming not just compute, but power, heat, installation space, noise, and maintenance access. IMMERSIA's immersion cooling — submerging electronics in compatible cooling fluid to remove heat — is one option for planning this compute infrastructure.
Immersion cooling itself has no function for classifying information or preventing external transmission. Information protection is achieved by combining network controls, authentication, software, permission management, and operations. Heat handling and installation conditions must also be confirmed per model, configuration, and site.
Making this distinction clear also clarifies who to consult. Business teams organise the information and tasks they need; IT designs access and routing; facilities confirms power, cooling, and maintenance. All three sharing the same concept leads to a deployment without unrealistic expectations.
Mixed information: separate the tasks
Suppose a sales rep is drafting a proposal combining a public catalogue with internal discount terms. Whether both documents can be sent to an external AI together depends on the most sensitive piece of information. The fact that most content is public does not allow the remaining confidential information to travel the same route.
One approach is to separate the task of writing the public-only description from the task of incorporating individual terms. Even so, the resulting text may still contain confidential content. Do not assume that processing makes output freely shareable — confirm where the final output will go.
Even on-premises AI may not be entirely free of external connections. Some configurations require communication for updates, monitoring, or licence verification. Keeping the data path and the management communication path distinct makes the scope of "processed internally" clear.
Early in planning, a single table listing information types, user departments, referenced systems, external-transmission permission, and responsible reviewers is useful. Leave ambiguous cells blank rather than forcing an answer — they become items to resolve before implementation, and they narrow the scope of PoC verification.
One more point: keeping processing on-premises is not the same as copying all data. You can reference the original business system, or prepare only the necessary scope for search. If you do copy, decide when updates and deletions are reflected so that outdated documents do not continue to serve as the basis for answers.
The starting point: "What stays on-premises?"
Hybrid AI is not a term for applying the same configuration to every organisation. It is a method of first deciding which information to protect and what the business goal is, then finding the combination that meets those conditions. There is no need to move everything on-premises, nor to send everything to the cloud.
For your next meeting, pick three documents you actually handle, and map out what may be sent externally and who is responsible for review. That small exercise becomes the concrete material for evaluating configurations and costs. Next time, we look at how to translate this policy into actual transmission controls and access management.